
Montana's organizations call us when something's gone wrong.
Big Sky Cybersecurity Inc. investigates breaches and helps reduce the risk of the next one, from offices in Great Falls, Billings and Helena and staff across the state.
When an insurer or an auditor asks who looked at your systems, our credentials are the ones they recognize.

We started this after watching it happen to a neighbor.
Big Sky Cybersecurity started with something we kept seeing in her own community: a local business hit by a cyberattack and a community business gone in months. Those weren't big companies with security teams. They were clinics, law firms, and small family run businesses that couldn't afford being down or the response. Today more than 50 organizations including clinics, law firms, accounting firms and small businesses rely on our team.
Big Sky Cybersecurity Inc. was founded in 2023 and is Montana owned and women owned (WOSB certified). Our team has supported Montana business and K12 technology since 2013 through Schoolhouse IT as well.
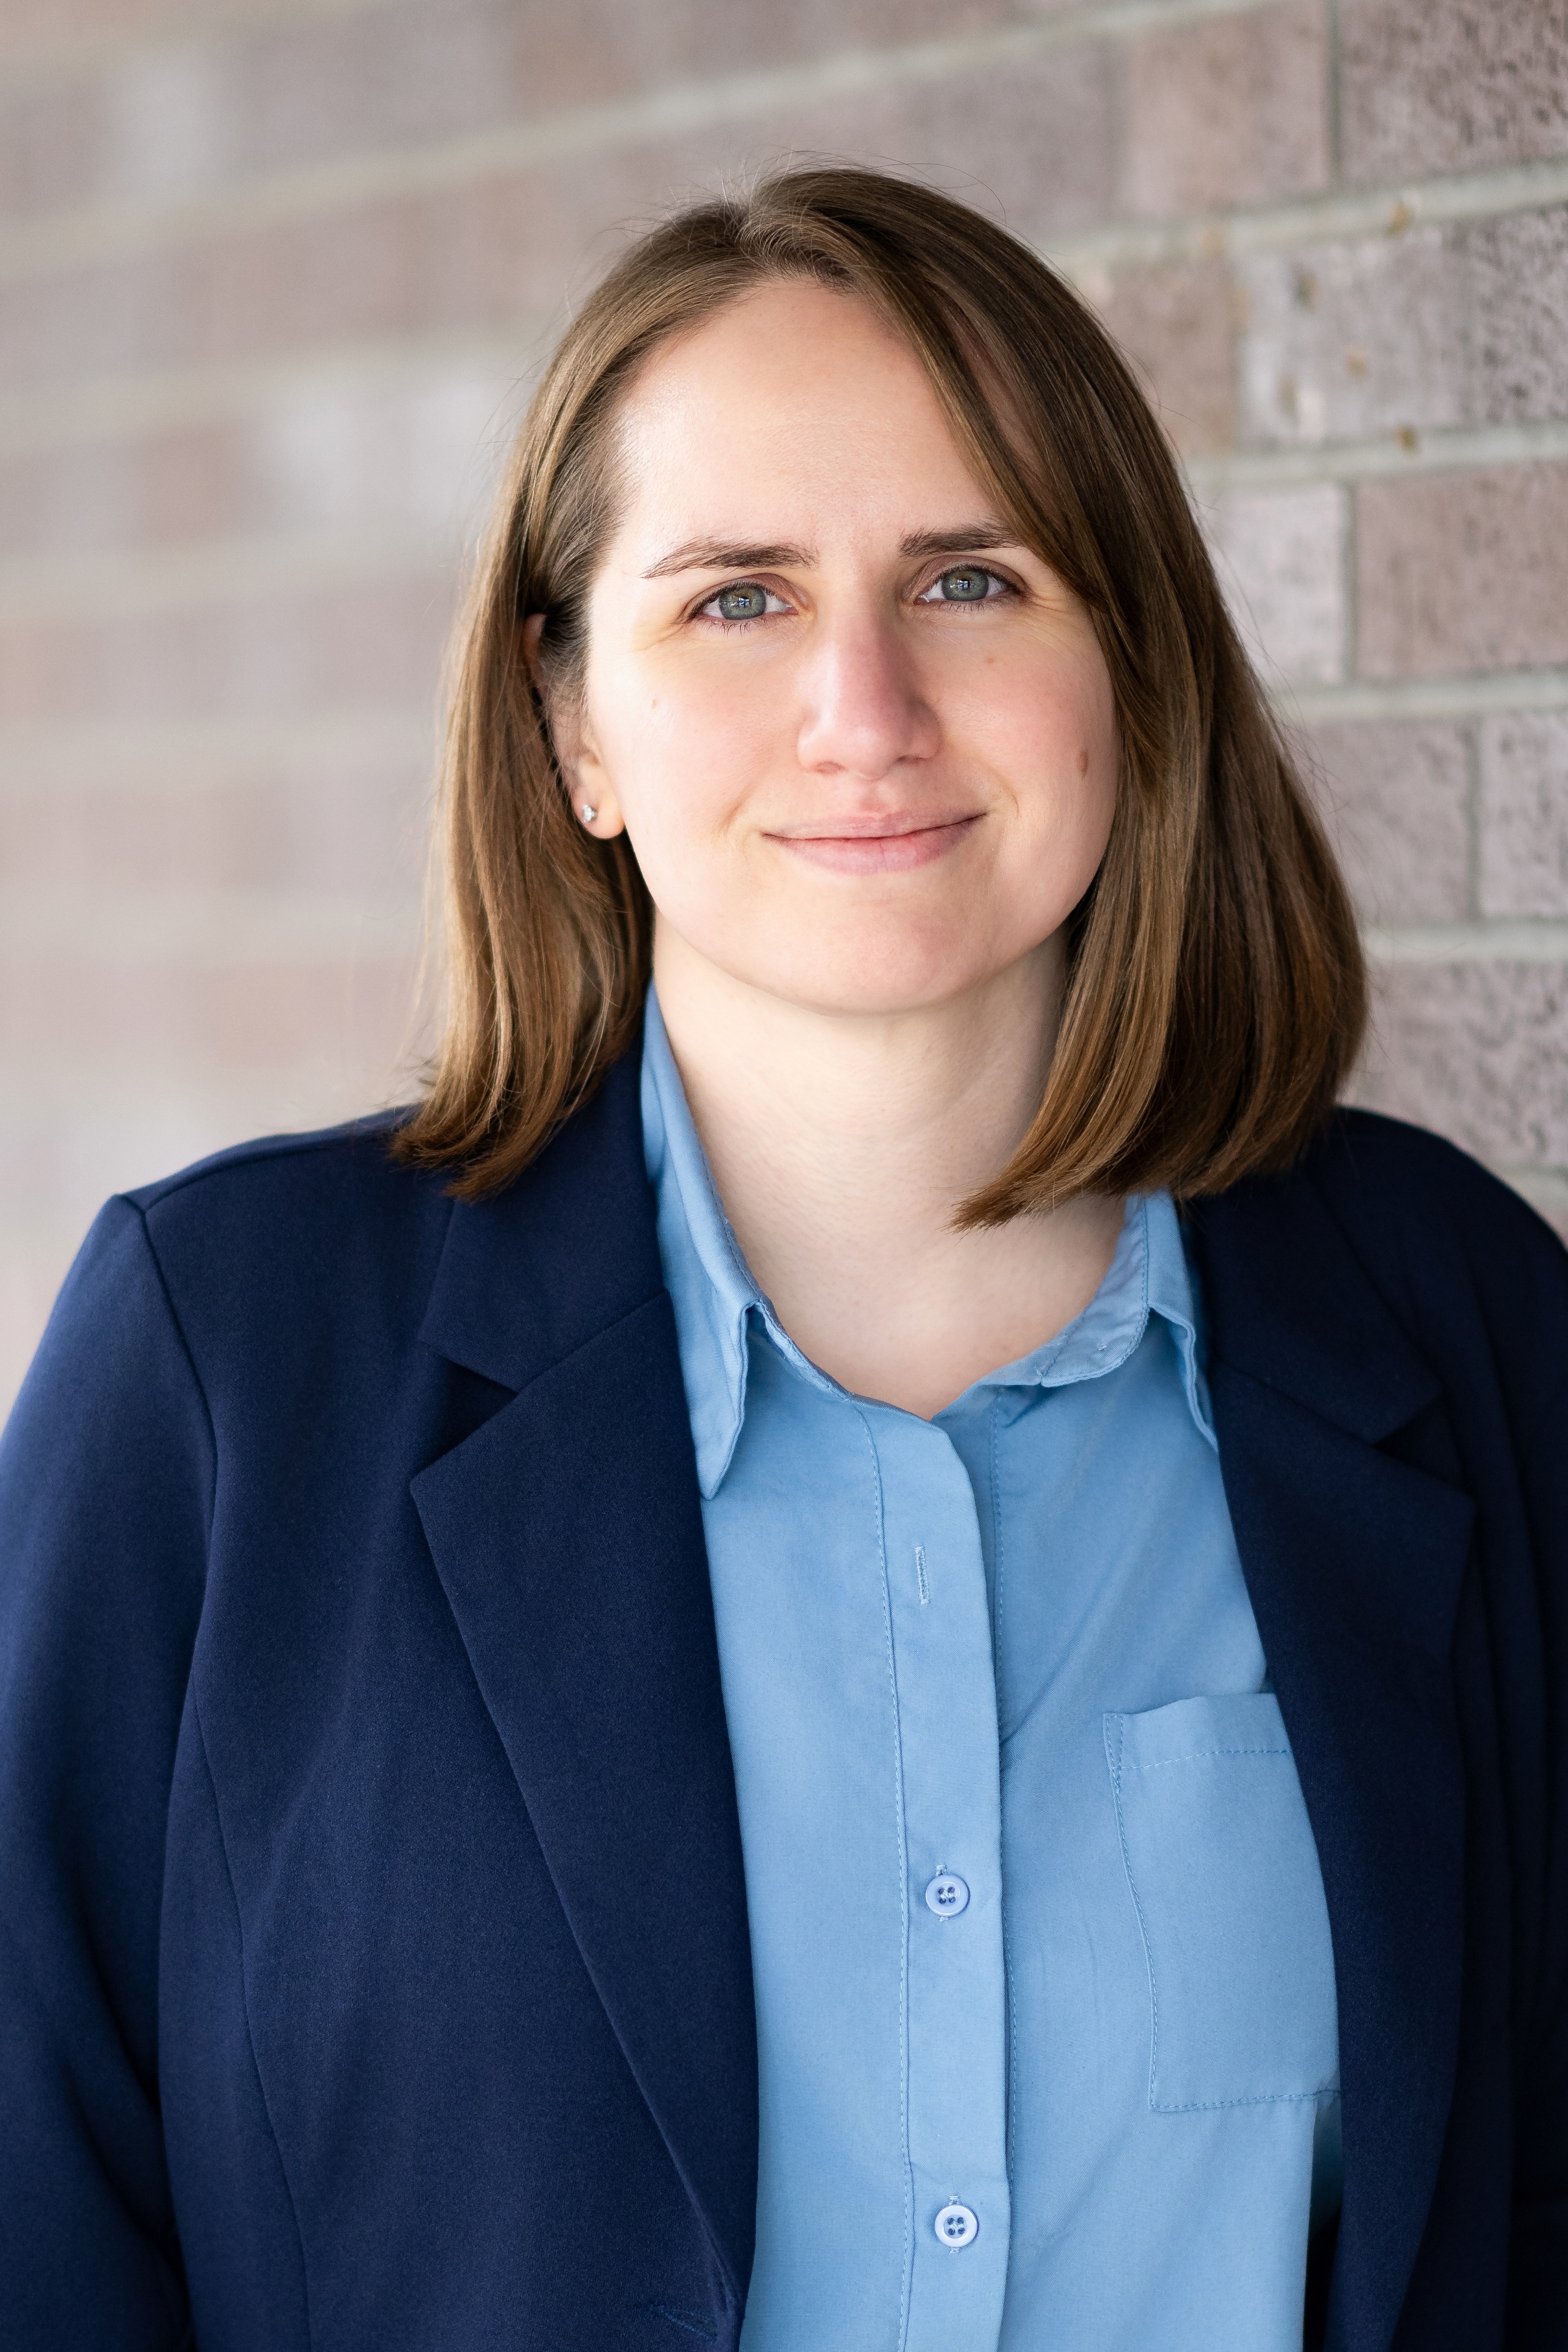
Dawn Van Zandt
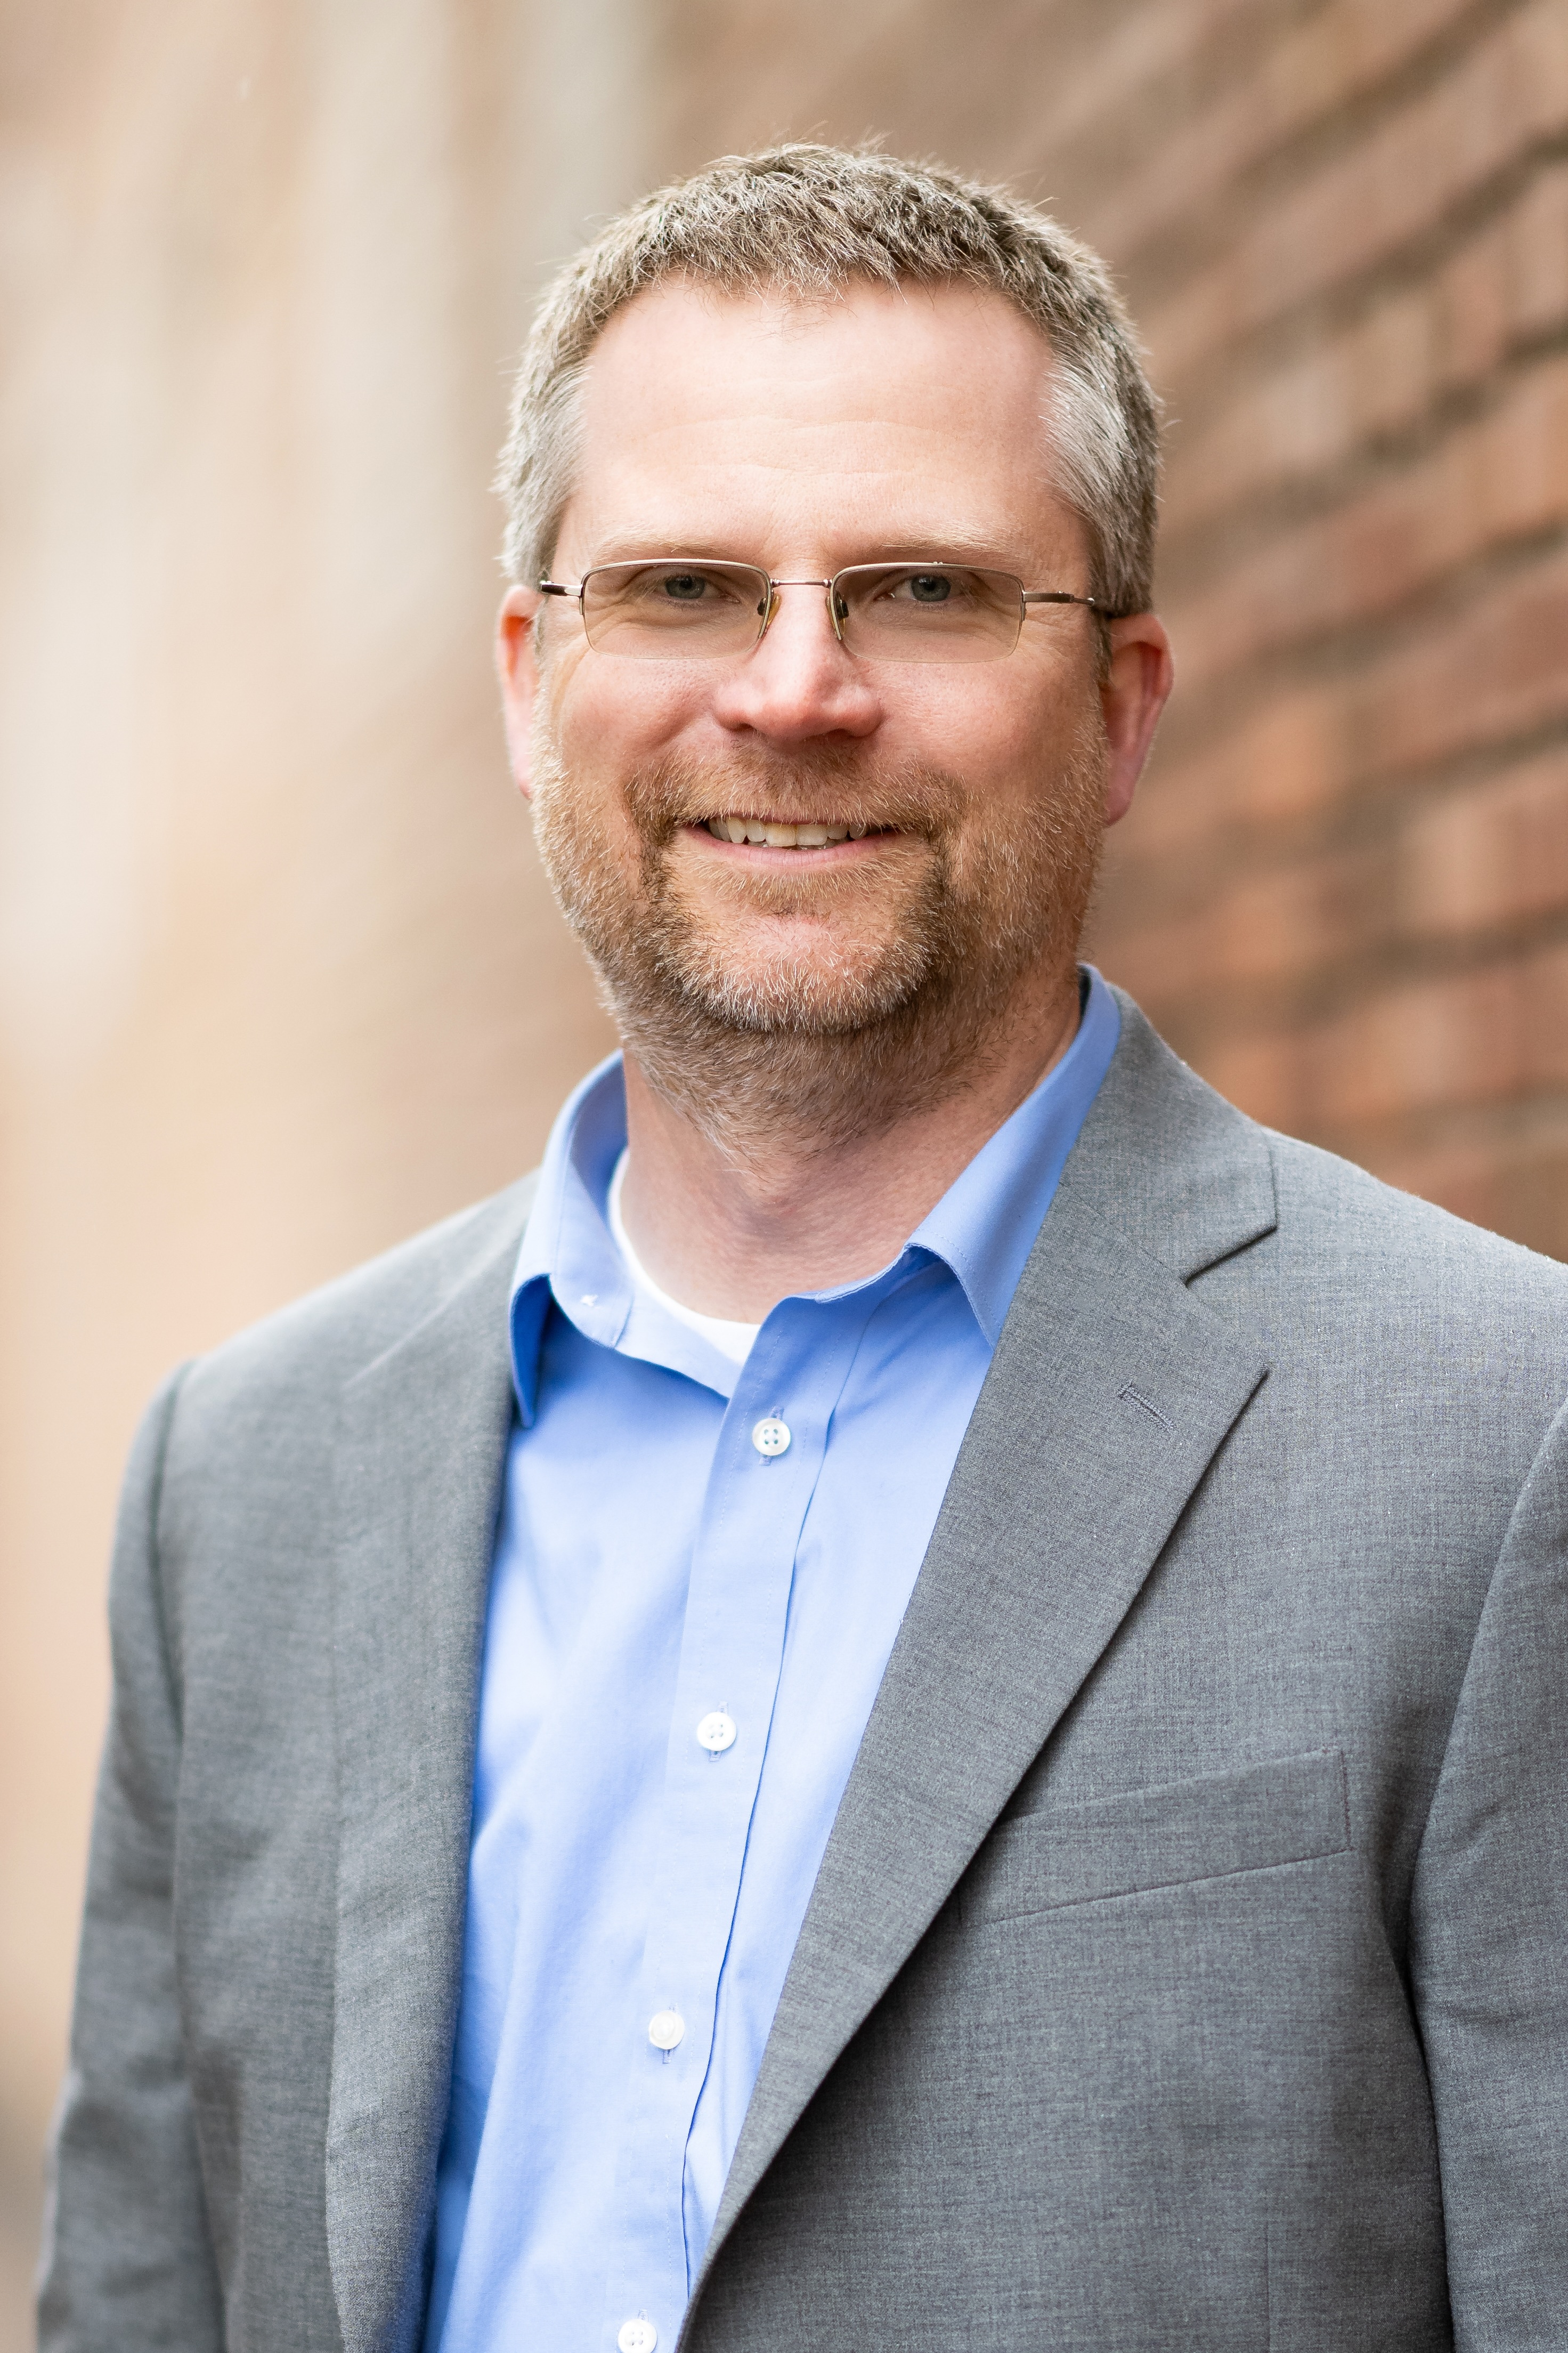
James Krippes
Three things guide every decision we make.
Secure every step
We fit the work to your business, not a template. Every change has a reason, and you'll know what it is.
Lead with expertise
We don't just do the work. We help you figure out what you actually need, then tell you straight, even when the answer is "you don't need us for that."
Protect today, plan for tomorrow
We fix what matters now and get you ready for what's coming next, without selling you things you don't need.
Sound familiar?
We hear the same frustrations from owners all over Montana. None of them are your fault, and every one of them has a fix you can see.
“
Your IT guy keeps coming out. It works while he's there but stays an issue.
What changes
We fix the cause, then show you the note that says what it was.
“
Somebody reboots the switch and it works again. Until Thursday.
What changes
We map the network first, and you keep the diagram either way.
“
You approve the invoice. You've never seen anyone check the backups.
What changes
Restores tested on a schedule, with the date written down.
“
The insurer's questionnaire takes three weeks to answer.
What changes
We answer it from evidence we already keep, usually in days.
“
Something breaks, and then a second bill arrives.
What changes
Flat monthly pricing, and every price is published.
“
Your one IT person is carrying the whole thing alone.
What changes
We back them up, without replacing them.
5 things we check every month. And what the report shows you.
Most incidents we respond to start with one of these five. Here’s how our standard handles each one, and what you see in your monthly report.
Patches applied on a schedule, including third party software, not only Windows.
Access removed when someone leaves, and every account reviewed each month.
Backups proven by restoring them every month, not just by checking that they ran.
Endpoint detection on every device, monitored by our team.
A five year roadmap of what’s aging out and when to budget for it, reviewed with you.
Three steps before anything changes.
With one of our security engineers. Nothing installed, nothing scanned.
What’s on your network and how it’s set up, onsite if it helps.
The findings are yours either way, whether we do the work or your current provider does.
Already have a provider? See exactly how switching works. It takes about two weeks, and nothing is touched until it’s documented.
The people behind your account.
The helpdesk
Your onsite engineer
Security monitoring
Forensics team
Training that covers forensics, offensive testing, and security operations.
Book a quick call with our team.
You describe what you need help with. We tell you whether it's a real risk or a nuisance. Nothing installed, nothing scanned.