
Healthcare IT and HIPAA Compliance in Great Falls, MT
Your practice has the same obligations as the hospital across town, on a fraction of its IT budget. We build the security and documentation to match, for practices of 3 to 20+ staff.
HIPAA trained, continuously. Everyone who works on your network understands the risk,
We sign a BAA before any work begins on your network or systems.
Our own HIPAA risk analysis and training records, held to the standard we document for you.
“Great company to work with. Any issues we have had they have addressed quickly.”
★★★★★
What we commit to.
Most practice incidents aren't sophisticated. What decides the cost is how fast we respond, and whether logs can show what was actually accessed.
Response commitments for certified practices
When the clock starts
At a confirmed event or your notification to us
Ransomware
Response within 1 hour
Business email compromise
Response within 1 hour
Backup recovery failure
Response within 4 hours
Nights and weekends
The same commitments hold
If it needs hands
Onsite the same day for contract clients
We do the work
The Big Sky Guarantee
For certified practices on our Professional package or co-managed services, The Big Sky Guarantee is our commitment to do the response work ourselves, at no additional cost, within defined service limits.
+
We back it in writing
The Big Sky Service Warranty
A separate written warranty on our managed services, with eligible payments made directly to your practice, up to $500,000 per covered incident, depending on your plan.
Eligibility requirements, service limits and exclusions apply. Full terms are provided for your review before you sign. Neither is an insurance policy, and the warranty does not replace cyber insurance.
A hospital has a compliance team. You have an office manager.
An illustrative week for the person who inherited IT because nobody else was supporting it.
Mon
Credentialing
Billing
IT: printer offline
IT: phones intermittent no call
Tue
Prior authorizations
IT: vendor call
Billing
Scheduling
Wed
Credentialing
Prior authorizations
IT: new hire account setup
Billing
Thu
Scheduling
IT: insurer questionnaire
Billing
Prior authorizations
Fri
Billing
Scheduling
IT: EHR update on server
IT: PC updates across office
A hospital has a security officer, an IT department and a compliance team for the red boxes. Your practice has whoever is free. Insurers still ask you the same questions, and a breach of 500 or more patients triggers the same notice requirements from HIPAA. The state has other privacy laws with different notification rules.
The rule everyone's warning you about isn't law yet.
As of September 2026, the proposed HIPAA Security Rule update is not final. Here's what actually affects your practice.
Nothing new is required yet.
If it finalizes, you get 60 days until it takes effect and roughly 180 more to comply. That may not be enough to encrypt every endpoint, deploy MFA and redesign backups at a price you control.
Be wary of anyone selling urgency.
Already required today
Current risk analysis
Asset inventory
MFA
Verified encryption
Annual BAA review
All five are required by the rule in force, so none of it is spent on a maybe. An outdated or missing risk analysis is the most common finding in the practices we assess.
What we handle for your practice.
Everything around the EHR, so your office manager gets their afternoons back to focus on what the staff and practice needs.
Why it matters who touches your network
Our technicians are trained on HIPAA continuously
Moving a folder or silencing an audit alert can create a HIPAA finding. Everyone who works in your practice is trained on what the Security Rule requires, on an ongoing basis.
We hold ourselves to the same standards we help our clients meet.
EHR adjacent infrastructure
Workstations, interfaces, imaging, printing and the vendor calls. We don't replace your EHR vendor.
Access control
Front desk, clinical and billing each see only what they need. Terminations processed the same day, everywhere.
MFA and encryption
On remote access, email and the EHR, including laptops that go home. The two controls insurers ask about first.
Audit logging
Who accessed what, and when. During an investigation it is the only thing that establishes what was reached.
Security risk analysis and evidence
The deficiency OCR cites most often. We produce the technical portion and the evidence.
Who we work with in Great Falls.
Six kinds of practice, each with its own weak spot, plus the hospitals they refer to.
One contact, five vendors
Primary care and specialty
One point of contact for the EHR, practice management, clearinghouse, lab interface and portal.
Legacy imaging
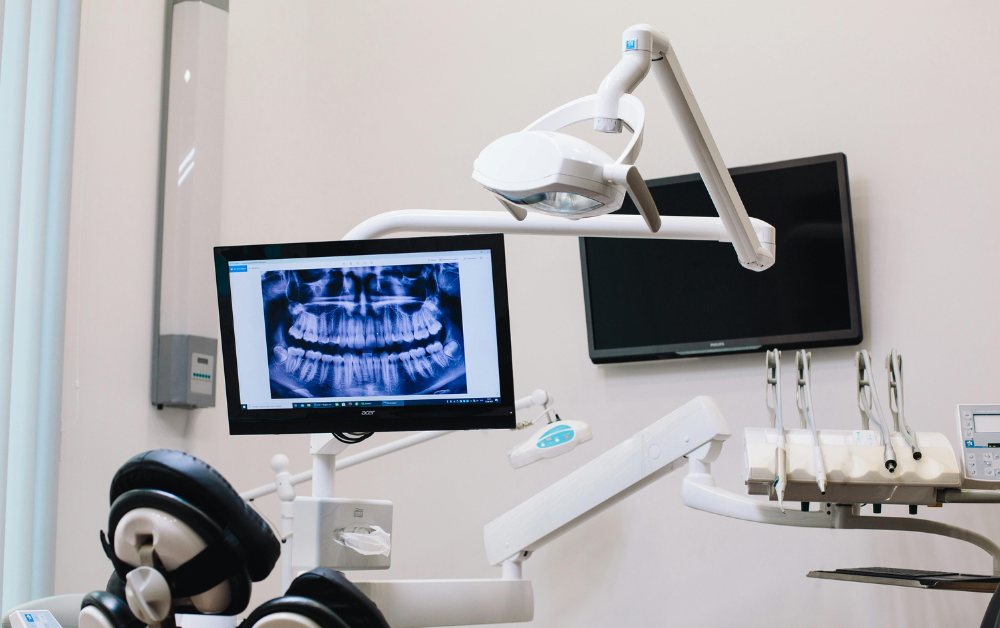
Dental practices
Keep the imaging software your vendor won't update, safely: isolated behind segmentation, with documented compensating controls.
42 CFR Part 2
Behavioral and mental health
Confidentiality for your most sensitive records, including 42 CFR Part 2 and telehealth outside the office.
Shared workstations
Therapy and outpatient clinics
Scheduling that stays up and shared workstations that log in fast, so nobody shares a password to keep the day moving.
Vendor equipment
Imaging, optometry and labs
Vendor controlled equipment on its own segment, large file transfers that work, and a written record of who owns what.
For hospitals
Hospitals and the practices tied to them
Practices answer a referral partner's security questions with documentation, not a scramble. Hospitals bring us in for penetration testing and a DFIR retainer alongside their own IT team.
Penetration testingDFIR retainerWhen the schedule stops: backup and recovery.
An illustrative Monday, with a plan in place
7:40
The EHR won't load and the front desk can't check anyone in. Staff open the printed downtime card.
7:45
Patients check in on paper, and someone calls the first appointments of the day.
Next
We restore in the order you agreed in advance, starting with practice management.
After
Paper charts are reconciled using the written procedure, not a week of guesswork.
What makes that Monday possible
Restoration order decided in advance. Nobody decides under pressure which server comes back first.
Recovery targets tied to your schedule. A Monday morning outage and a Friday evening outage are different problems.
Immutable, offsite backup copies. An attacker holding domain credentials can't delete your recovery path.
Documented downtime procedures. What staff do on paper, how it is reconciled, who calls patients.
Restore testing. A backup nobody has tested is not one that can be trusted.
How we take over from your current IT provider.
Whether you're leaving a provider or have no real IT support at all, we run in parallel until the handover is done.
Days 1 to 15
Days 15 to 30
Days 30 to 60
Days 60 to 90
Big Sky
Big Sky
Big Sky
Big Sky
Your current help
You keep the documentation either way
We sign a Business Associate Agreement before we touch anything containing ePHI. The inventory, documentation and network map we build in the first two weeks are shared with your team, and if you leave in two years they go with you. We overlap with your current provider until the handover is finished, so no one is left without support and no clinic day gets rescheduled around a cutover. Most transitions complete in about four weeks.
“Seamless, with absolutely no down time in the transition.”
Tera R. · Google review
Why practices work with us.
Six reasons, and the numbers behind them.
30+
Years of combined experience
in cybersecurity and technology, across our team
50+
Organizations supported
across Montana
5.0
On Google and Birdeye
Technicians trained on HIPAA continuously
The person changing a permission knows what it means for your compliance posture.
We know what a small practice can absorb
Enterprise tooling for an eight person clinic isn't security advice. It's a way to make sure nothing gets implemented.
Informed by forensics and incident response
We've handled the aftermath in healthcare. That changes what we prioritize beforehand.
Evidence, not assurances
Documentation you can hand to an insurer, an auditor or a referral partner.
References on request
Ask for Great Falls healthcare references on the first call. You'll get local names.
We sign a BAA
We hold ourselves to the same risk analysis and training standard as your practice.
Questions Great Falls practices ask.
Will you sign a Business Associate Agreement?
Yes, on every engagement, before we have access to any system that touches ePHI. Your IT provider is a business associate under HIPAA whether or not anyone signs anything — the agreement just puts the obligations in writing. If a provider hesitates on this question, that tells you something.
Do you work with our EHR vendor?
Yes. We coordinate with EHR and practice management vendors as part of the service — support tickets, interface issues, upgrade scheduling, and the back-and-forth that otherwise lands on your office manager.
Ransomware is our biggest worry. What actually protects us?
Three things in order: backups an attacker cannot reach, MFA so the credential theft that precedes most ransomware doesn't work, and monitoring that catches the activity before encryption starts. For certified practices with the required controls in place, The Big Sky Guarantee and The Big Sky Service Warranty also apply. Eligibility requirements, service limits and exclusions apply, and full terms are provided for your review before you sign. Neither replaces the controls themselves.
Do we need to act on the proposed HIPAA Security Rule changes now?
Not yet, but don't wait either. The five foundational items are already required under the Security Rule in force today, so doing them now costs nothing extra and removes most of the pressure if the rule finalizes with a 240-day compliance clock.
We just failed a cyber insurance renewal questionnaire. Can you help?
One of the most common reasons practices call us. The questions typically cover MFA, endpoint detection, backup testing, email filtering, and training. We implement what's missing and give you documentation to answer with.
We have an old imaging or practice management system the vendor won't update. What then?
Common in dental and imaging, and not a reason to give up. When a system can't be secured directly, we isolate it so it can't be used as a path into everything else, and document the compensating controls.
We're a four-provider practice. Are we too small?
No. Small practices are targeted specifically because attackers assume the controls aren't there.
What happens if we have a breach?
Containment first, then forensic scoping to establish what was actually accessed — which is what determines your notification obligations. See the breach response section above for how that works.
Do you support clinics outside Great Falls?
Yes, throughout Central Montana including Fort Benton, Choteau, Conrad, Stanford, and Lewistown. Multi-site practices are common here and remote management covers most day-to-day support.

Tell us about your practice and what isn't working.
The assessment is free. Thirty to forty-five minutes onsite, at a time you pick, and the findings are yours either way. We sign a BAA before we look at anything containing ePHI.
“James and his team at Big Sky Cybersecurity are an integral part of my business' team as they help to protect my business from various cyber threats.”
Chad M., accounting firm owner
Big Sky Cybersecurity provides healthcare IT support and HIPAA security services throughout Great Falls and Cascade County, including Black Eagle, Belt, Cascade, Sun River, Vaughn, Simms, Fort Shaw, and Ulm, plus Central Montana communities including Fort Benton, Choteau, Conrad, Dutton, Augusta, Stanford, Geraldine, Highwood, and Lewistown.