Currently dealing with a breach or active incident?Call 406-924-3731×
≡
Cybersecurity audit — Great Falls, Billings and Helena

Your insurer is asking for an assessment. Here's what ours tells them.

Our report names the framework you're being held to, the gaps that matter most to your organization, and what each one costs to fix.

Onsite fieldwork, with no travel fee anywhere in Montana, carried out by our own engineers.

5.0 on Google & Birdeye★★★★★See what our clients are saying

Absolutely the best! This team is responsive, thorough, and has a great sense of humor.

Mary S.

What an amazing team! Instant response, thorough and professional. Thank you so much!

Tamara B.

Fantastic and timely support. Always professional with a great sense of humor!

Mary Anne S.

Great company to work with. Any issues we have had they have addressed quickly.

Kevin F.

James is great to work with! We appreciate their expertise and timely responses.

Teresa W.

…They made themselves available until the issue was addressed and remedied.

Michael W.

…They understand that small communities have different needs than large organizations.

Loren T., Mayor of Fairfield

…Consistently goes above and beyond to support our needs as a non-profit.

Melissa T.

…Seamless, with absolutely no down time in the transition.

Tera R.

…They tailor everything to your needs. They help my business run smoothly.

Jessica J.

Exceptional to work with, and have met all of the requests we have placed with them.

Kenneth M.

Great company, very helpful and professional. Always eager to assist with an issue.

Eric P.

…The support is efficient and effective. Highly recommend for anyone needing IT support.

Andrew S.

…Dawn and James are eager to help us get our system on track again.

Ashley B.
Two colleagues reviewing audit findings together

★★★★★ 5.0 on Google and Birdeye · Most audits run 7 to 14 business days

7–14 days
Typical start to report
four steps, scoped on the call
100+
Incidents supported
by our team
Since 2013
Our team serving Montana
supporting businesses and nonprofits across the state
Audit requests

Nobody just starts looking for an audit.
You’re here because someone asked.

Your cyber insurer

The renewal came back with a questionnaire

Either one you can't honestly answer, or a renewal price that moved sharply. The insurer wants documented evidence of controls, not a promise that they exist.
They want
Evidence you can attach to the application.
Your clients

A 140 question vendor security review

Sent by their security team, with the contract renewal waiting until it's completed and returned.
They want
Answers backed by something, returned quickly.
A regulator

A named framework, not an audit in general

HIPAA requires a Security Risk Analysis. PCI DSS, GLBA, CMMC and SOX each want something different. Getting the wrong assessment is the same as getting none.
They want
The specific assessment their rule names.
Your board, or your own intuition

Somebody nearby got hacked

And you realized you don't actually know what you would lose, or how well you're protected right now.
You want
A straight answer before someone else forces one.
Pricing

What it costs,
and who each tier suits

Published starting prices for each scope. Tell us who asked for the audit and we’ll send a scoped number in one email.

Audit scopePriceBest for
Focused security auditStarting at $2,500Single site, no regulated data
Audit aligned to a frameworkStarting at $6,500You're being measured against HIPAA, PCI DSS, CMMC, or GLBA
HIPAA Security Risk AnalysisStarting at $6,500 for organizations that aren't clientsHealthcare practices meeting the HIPAA SRA requirement
Multisite or enterpriseScoped quoteMultiple locations, or a larger endpoint estate

What moves the price: number of locations, number of endpoints, whether regulated data is in scope, and whether you need us to sit with your auditor afterward. Nothing else.

Case study

A new director inherited the systems.
Nobody had written down how they worked.

What an audit looked like for one Montana organization handling sensitive client data, and what came after it.

Montana nonprofit

Handles sensitive client information. Led by a new executive director who inherited an unclear mix of technology, policies and procedures.

Technology audit · HIPAA gap assessment · policy development · staff training
Every unit
Business units interviewed directly during the audit
All staff
Trained on the new privacy and security procedures
Custom
Policies and procedures written for this organization
Situation

Leadership needed a clear picture of where they stood: what technology staff actually used, how work got done, and where they fell short on HIPAA and data privacy.

Approach

A technology audit of systems, processes and workflows. We met each business unit directly rather than working only from documentation, and focused on the gaps against HIPAA and data privacy practice.

What changed

The findings became policies and procedures written for how the organization actually works, fitted to the tools it already had. Every staff member was trained on them.

Outcome

Technology and processes are documented and clear, and the executive director can focus on the organization’s work instead of IT concerns.

“Big Sky Cybersecurity consistently goes above and beyond to support our needs as a non-profit business. They are so responsive and always give us the level of support and expertise we need to keep our systems and data safe…”

Melissa T. — the Montana nonprofit in this case study
Honest fit

When we’re not a good fit

We’d rather tell you now than three weeks into fieldwork. We’re probably not the right call if:

01

You only need a checkbox

A cheap automated scan may satisfy a light touch review. It may not hold up with an auditor or a claim investigation. If that’s genuinely all you need, buy the scan.

02

You want the report to settle a dispute with your IT provider

We won’t soften the findings to avoid an awkward conversation. We’ll also tell you when your provider is doing good work, which happens more often than you’d expect.

03

You expect the audit alone to fix it

The audit tells you what’s wrong and what it costs to fix. Fixing it is a separate decision and a separate budget.

Who is measuring you

Find your standard.
That’s the audit you need.

Findings are mapped to whichever standard is actually being applied to you, so you can hand the relevant section straight to whoever asked.

HIPAA

Security Risk Analysis for clinics and the vendors who serve them.

PCI DSS

Card handling, the donate button, the terminal in reception.

CMMC and NIST 800-171

Gap assessment and readiness work for the defense supply chain, with documentation for your assessor. We don’t certify.

GLBA

Written security plan for accounting firms and lenders.

CIS Controls

No regulator, just a board or an insurer asking.

Not sure which applies?

Tell us who is asking and we’ll name the standard on the call.

How it runs

Four steps, typically 7 to 14 business days

Scoped on the call, done in your building, delivered as a report and a readout.

01

Scoping call

15 to 20 minutes. Who is requiring the audit, what your environment looks like, and which scope you need.

02

Onsite fieldwork

Configurations read, documentation reviewed, your people interviewed. Anything carrying downtime risk is scheduled with you in advance.

03

Findings report

Mapped to your standard, costed per finding, ordered by risk reduction per dollar.

04

Readout

We walk your team through it live, and repeat it for your board or your insurer at no extra cost.

How we run it: fieldwork in your building by our own engineers, and no findings shared with your IT provider without your written go-ahead.

What you get

What lands in your inbox when the audit is done

A page from the report

Every finding states what it is, what an attacker or auditor would do with it, how to close it, and what it costs to close. No CVSS scores without translation, no raw scanner dumps padded to look thorough.

The remediation plan orders these by risk reduction per dollar, and the highest value items are marked as the ones to do this quarter.

What you receive when the audit closes

A findings report

A prioritized remediation plan

Evidence you can submit

A readout call

Findings report — redacted sample

HIGH

Domain admin accounts without MFA

One reused password reaches every server. Effort and cost to close are stated per finding.

MEDIUM

Backups never tested with a restore

The job reports success nightly. Nobody has opened the file since install.

LOW

Guest wifi shares the office VLAN

Illustrative layout. Severity labels and mapped controls follow the standard being applied to you.

Why us

The people writing your report are the people who’d investigate the breach

Findings written by people who investigate breaches

The engineers writing your report reconstruct real incidents, so each finding reflects how controls actually fail.

GIAC GCFA, GCFE and GNFA — forensic certifications

Each finding says what an attacker could do with it

We also run penetration tests, so the report explains the practical consequence, not just the control that’s missing.

CompTIA PenTest+ and GIAC GCIH

Fieldwork in your building, by our own engineers

We drive to you, and no part of the fieldwork is handed to anyone else.

Offices in Great Falls, Billings and Helena

Independent findings

Nothing in the report is written to sell you our managed services, and the plan works whoever does the fixing.

Plan written to be executable by your provider, your team or us

Certifications held by our engineers: CISSP, GIAC GCFA, GCFE, GNFA and GCIH, CEH, CompTIA PenTest+, CySA+ and Security+, SSCP and CNSP.

FAQ

Frequently asked questions

How long does an audit take?

Most audits run 7 to 14 business days from the start of fieldwork to the delivered report.

Will it disrupt our operations?

Almost never. Most of the work is reading configurations, reviewing documentation, and talking to your people. Testing that carries any risk of downtime is scheduled with you in advance and never runs unannounced.

What if you find something bad? Does that hurt my insurance?

A documented finding with a remediation plan attached is generally a stronger position than an unanswered questionnaire. Your insurer or broker can confirm how they treat it.

Who sees the report?

You. We don't share findings with anyone — including your IT provider — without your written go-ahead.

Is this a sales pitch for managed IT?

Most audit clients never move to our managed services, and the report doesn't change either way.

Do you do the remediation too?

We can, or your existing provider can, or your internal team can. The plan is written to be executable by whoever you choose.

Is an audit the same as a penetration test?

No. An audit examines your systems, policies, and procedures against a standard. A penetration test attacks you to see what breaks. Most people asked for an audit need an audit. If you need both, bundling them is cheaper.

How often should we do this?

Annually for most organizations, and whenever a framework, contract, or insurer requires it. More often if you've changed locations, systems, or headcount significantly.

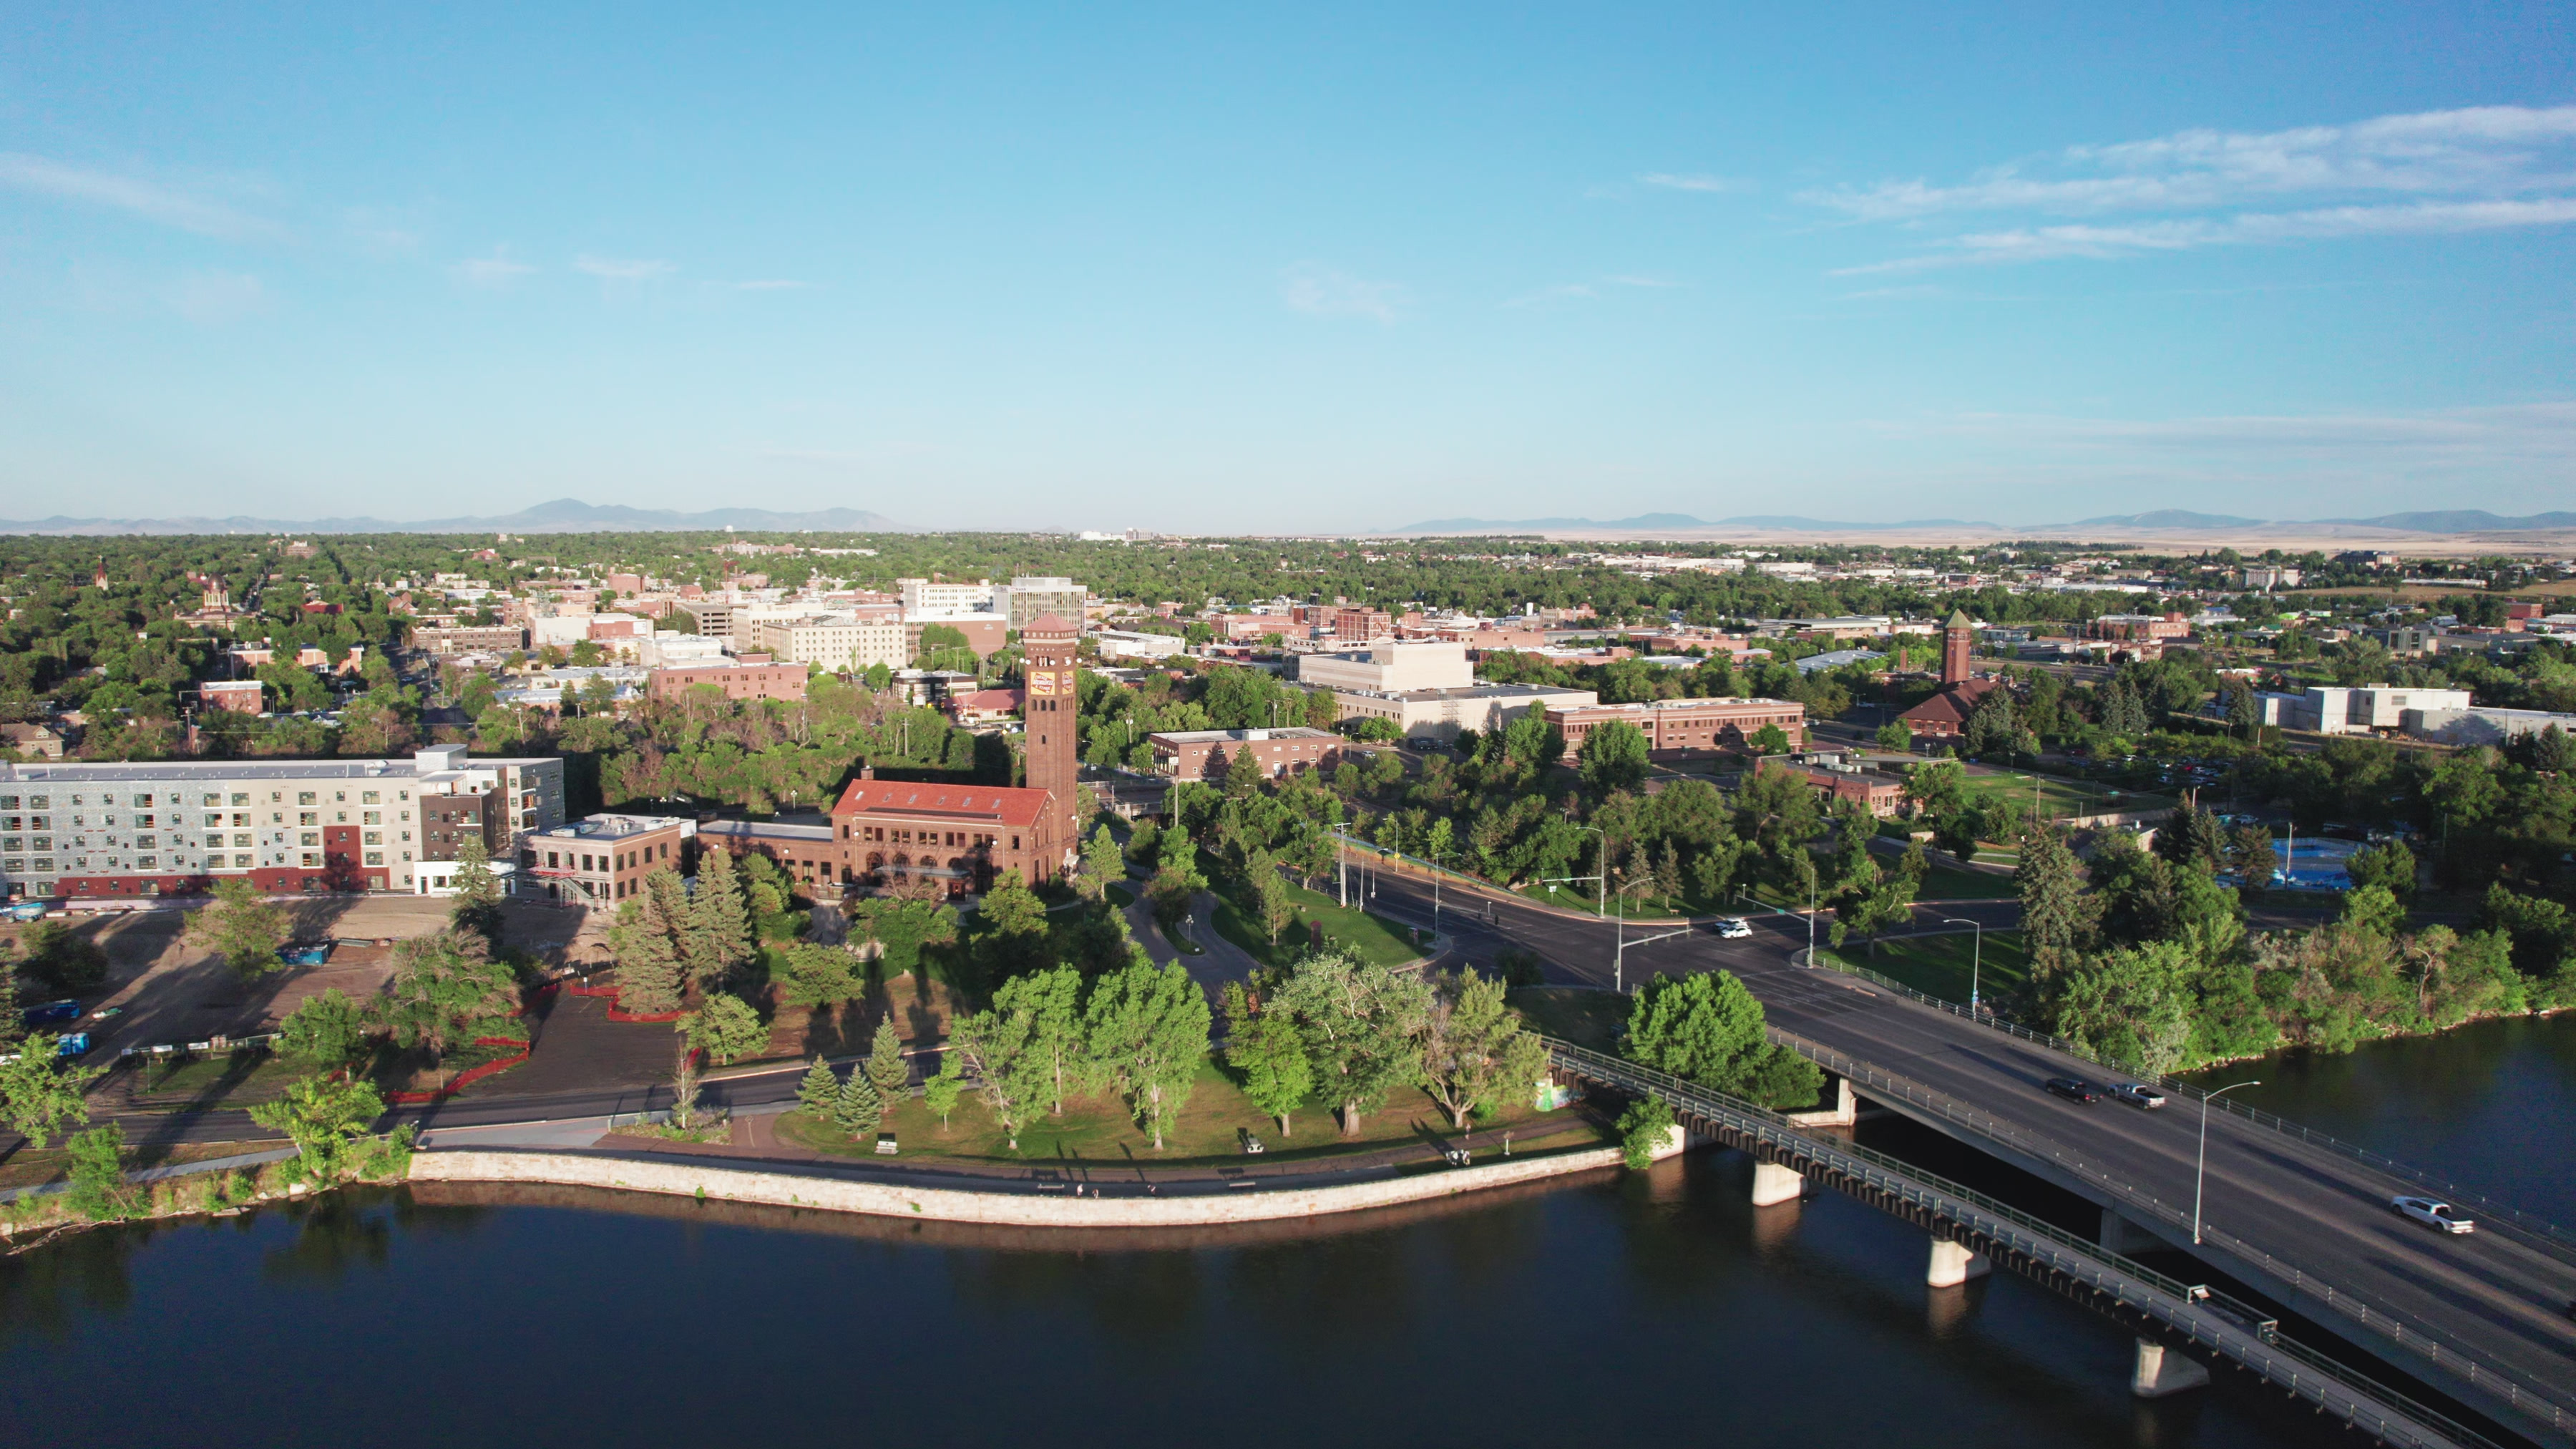
Aerial view of Great Falls, Montana
Next step

Find out which audit you need, and what it costs

01
Ready to scope it

Send the form. An engineer reads it and replies with the scope you need and a price.

02
Not sure yet

Call 406-924-3731 for a 15 to 20 minute call. Tell us who asked for the audit and we’ll name the standard, with no commitment.

03
Comparing prices

Our starting prices are published on the pricing page.

Call Us At

406-924-3731
Rated★★★★★5.0

…Given that I was 11 time zones from Great Falls, they made themselves available until the issue was addressed and remedied. They have great expertise and are more than willing to provide exceptional service to their clients. I highly recommend them.

Michael W.

…The Town of Fairfield has worked with Big Sky to develop and implement a comprehensive cybersecurity system to protect the Town's technology, data, and day-to-day operations… they understand that small communities have different needs and resources than large organizations.

Loren T., Mayor of Fairfield

Big Sky Cybersecurity has been exceptional to work with and have met all of the requests we have placed with them.

Kenneth M.

Big Sky Cybersecurity consistently goes above and beyond to support our needs as a non-profit business. They are so responsive and always give us the level of support and expertise we need to keep our systems and data safe…

Melissa T.

…We transitioned from an in house server to a cloud based server and it has been seamless and absolutely no down time in the transition. Lots of steps to take but they made it super easy and fun to do.

Tera R.

James has been very attentive to updating our systems and helping us roll out new features company wide. The support is efficient and effective, highly recommend for anyone needing I.T. support.

Andrew S.

This company is so wonderful to work with. They tailor everything to your needs. They are very accessible and easy to talk to… I could not say enough good things, they help my business run smoothly.

Jessica J.

…Even though we call because we have a problem, Dawn and James are eager to help us get our system on track again. Would highly recommend for anyone wanting fantastic service.

Ashley B.

Great company, very helpful and professional. James is great at what he does and always eager to assist with an issue.

Eric P.

James is great to work with! We greatly appreciate their expertise and timely responses to any issues or concerns!

Teresa W.

Absolutely the best! This team is responsive, thorough, and has a great sense of humor. We couldn't live without them!

Mary S.

Great company to work with. Any issues we have had they have addressed quickly.

Kevin F.

What an amazing team! Instant response, thorough and professional. Thank you so much!

Tamara B.

Fantastic and timely support. Always professional with a great sense of humor!

Mary Anne S.

See what our clients are saying
Sent. An engineer will reply by email with your scope.
That didn’t send. Call 406-924-3731 and we’ll pick up.

Audits delivered onsite from Great Falls, Billings and Helena. Starting at $2,500.